
The fraud threat landscape for short-term rental operators has fundamentally changed. Fraudulent actors no longer rely on stolen credit cards. They use fully synthesized identities constructed from fragmented data — AI-generated faces, fabricated government documents, and authentic compromised payment credentials combined into profiles that look completely legitimate on paper.
By 2026, security analysts report that AI-generated deepfakes successfully bypass legacy static ID verification in 68% of fraudulent short-term rental booking attempts. A JPEG upload of a driver's license is no longer sufficient proof of identity. And the financial consequences of failing to catch these synthetic identities are severe: the average cost of a retaliatory chargeback following a fraudulent booking now exceeds $4,200 per incident, factoring in reversed transactions, processor penalties, and the internal cost of managing disputes.

How Deepfakes Defeat Standard Screening
Legacy guest screening typically asks guests to upload a photo of their ID alongside a static selfie. These systems compare the images against the reservation data. The process contains a fundamental vulnerability: it assumes the uploaded file is an unedited photo of a physical document.
Fraudsters exploit this assumption with generative AI. Given a stolen cardholder's name and billing address, they use AI image generation to create a photorealistic synthetic face, then apply digital manipulation tools to place that face — and the stolen personal data — onto a realistic ID template. The result passes visual inspection and basic automated checks. The lighting is correct, the micro-printing looks authentic, the facial proportions are flawless.
Manual review can't catch these manipulations. And if your screening stops at static image analysis, a sophisticated fraudster gains property access without ever revealing their real identity.
Red Flags That Indicate High-Risk Bookings
While AI can fabricate identity documents, behavioral patterns often reveal malicious intent. Short-term rental fraud tends to follow predictable patterns:
Local addresses that match or are very close to the property location — fraudsters need a venue in their immediate area to host events without using their own home. Last-minute reservations within 24 hours of check-in — designed to exploit operational urgency and rushed approval processes. High-value property selections with expansive spaces suited to larger gatherings. Refusal to complete pre-arrival workflows, ignored digital guidebook links, and use of burner phone numbers.
These signals alone aren't definitive, but in combination with weak verification they indicate properties that are being specifically targeted for their security gaps.
Why Chargebacks Are So Hard to Win Without Data
When a fraudster successfully books, causes damage, and then disputes the charge, the burden of proof falls entirely on the operator. A signed rental agreement and a photo ID — even if the ID looked legitimate — are easily dismissed by payment processors. Banks understand that static images can be fabricated with basic software.
To win chargeback disputes definitively, operators need objective, timestamped forensic data that banks cannot dismiss: biometric evidence that the verified guest was physically present, IoT sensor logs showing exactly when noise thresholds were breached, and digital contracts binding the guest's identity to the terms they violated.
Without this data, most operators lose these disputes even when they're clearly in the right.
The Zero-Trust Verification Model
Enso Connect's guest verification approach is built on a zero-trust architecture: every guest is verified, every check-in is conditional on successful verification, and property access doesn't unlock until all requirements are met.
Biometric liveness detection replaces static photo uploads with real-time verification. Instead of uploading a JPEG, guests are prompted to perform specific micro-movements while the system scans their face in three dimensions. Liveness detection analyzes skin texture, facial depth, and natural light reflection — characteristics that AI-generated deepfakes, which exist only as two-dimensional data, cannot replicate. Synthetic faces fail the liveness check immediately. Real guests pass in seconds.
Digital contracts bind the verified biometric identity to legally enforceable terms covering noise limits, occupancy caps, and damage policies. The signature is tied to the biometric scan, not just an email address. This creates an evidence chain that holds up in dispute resolution.
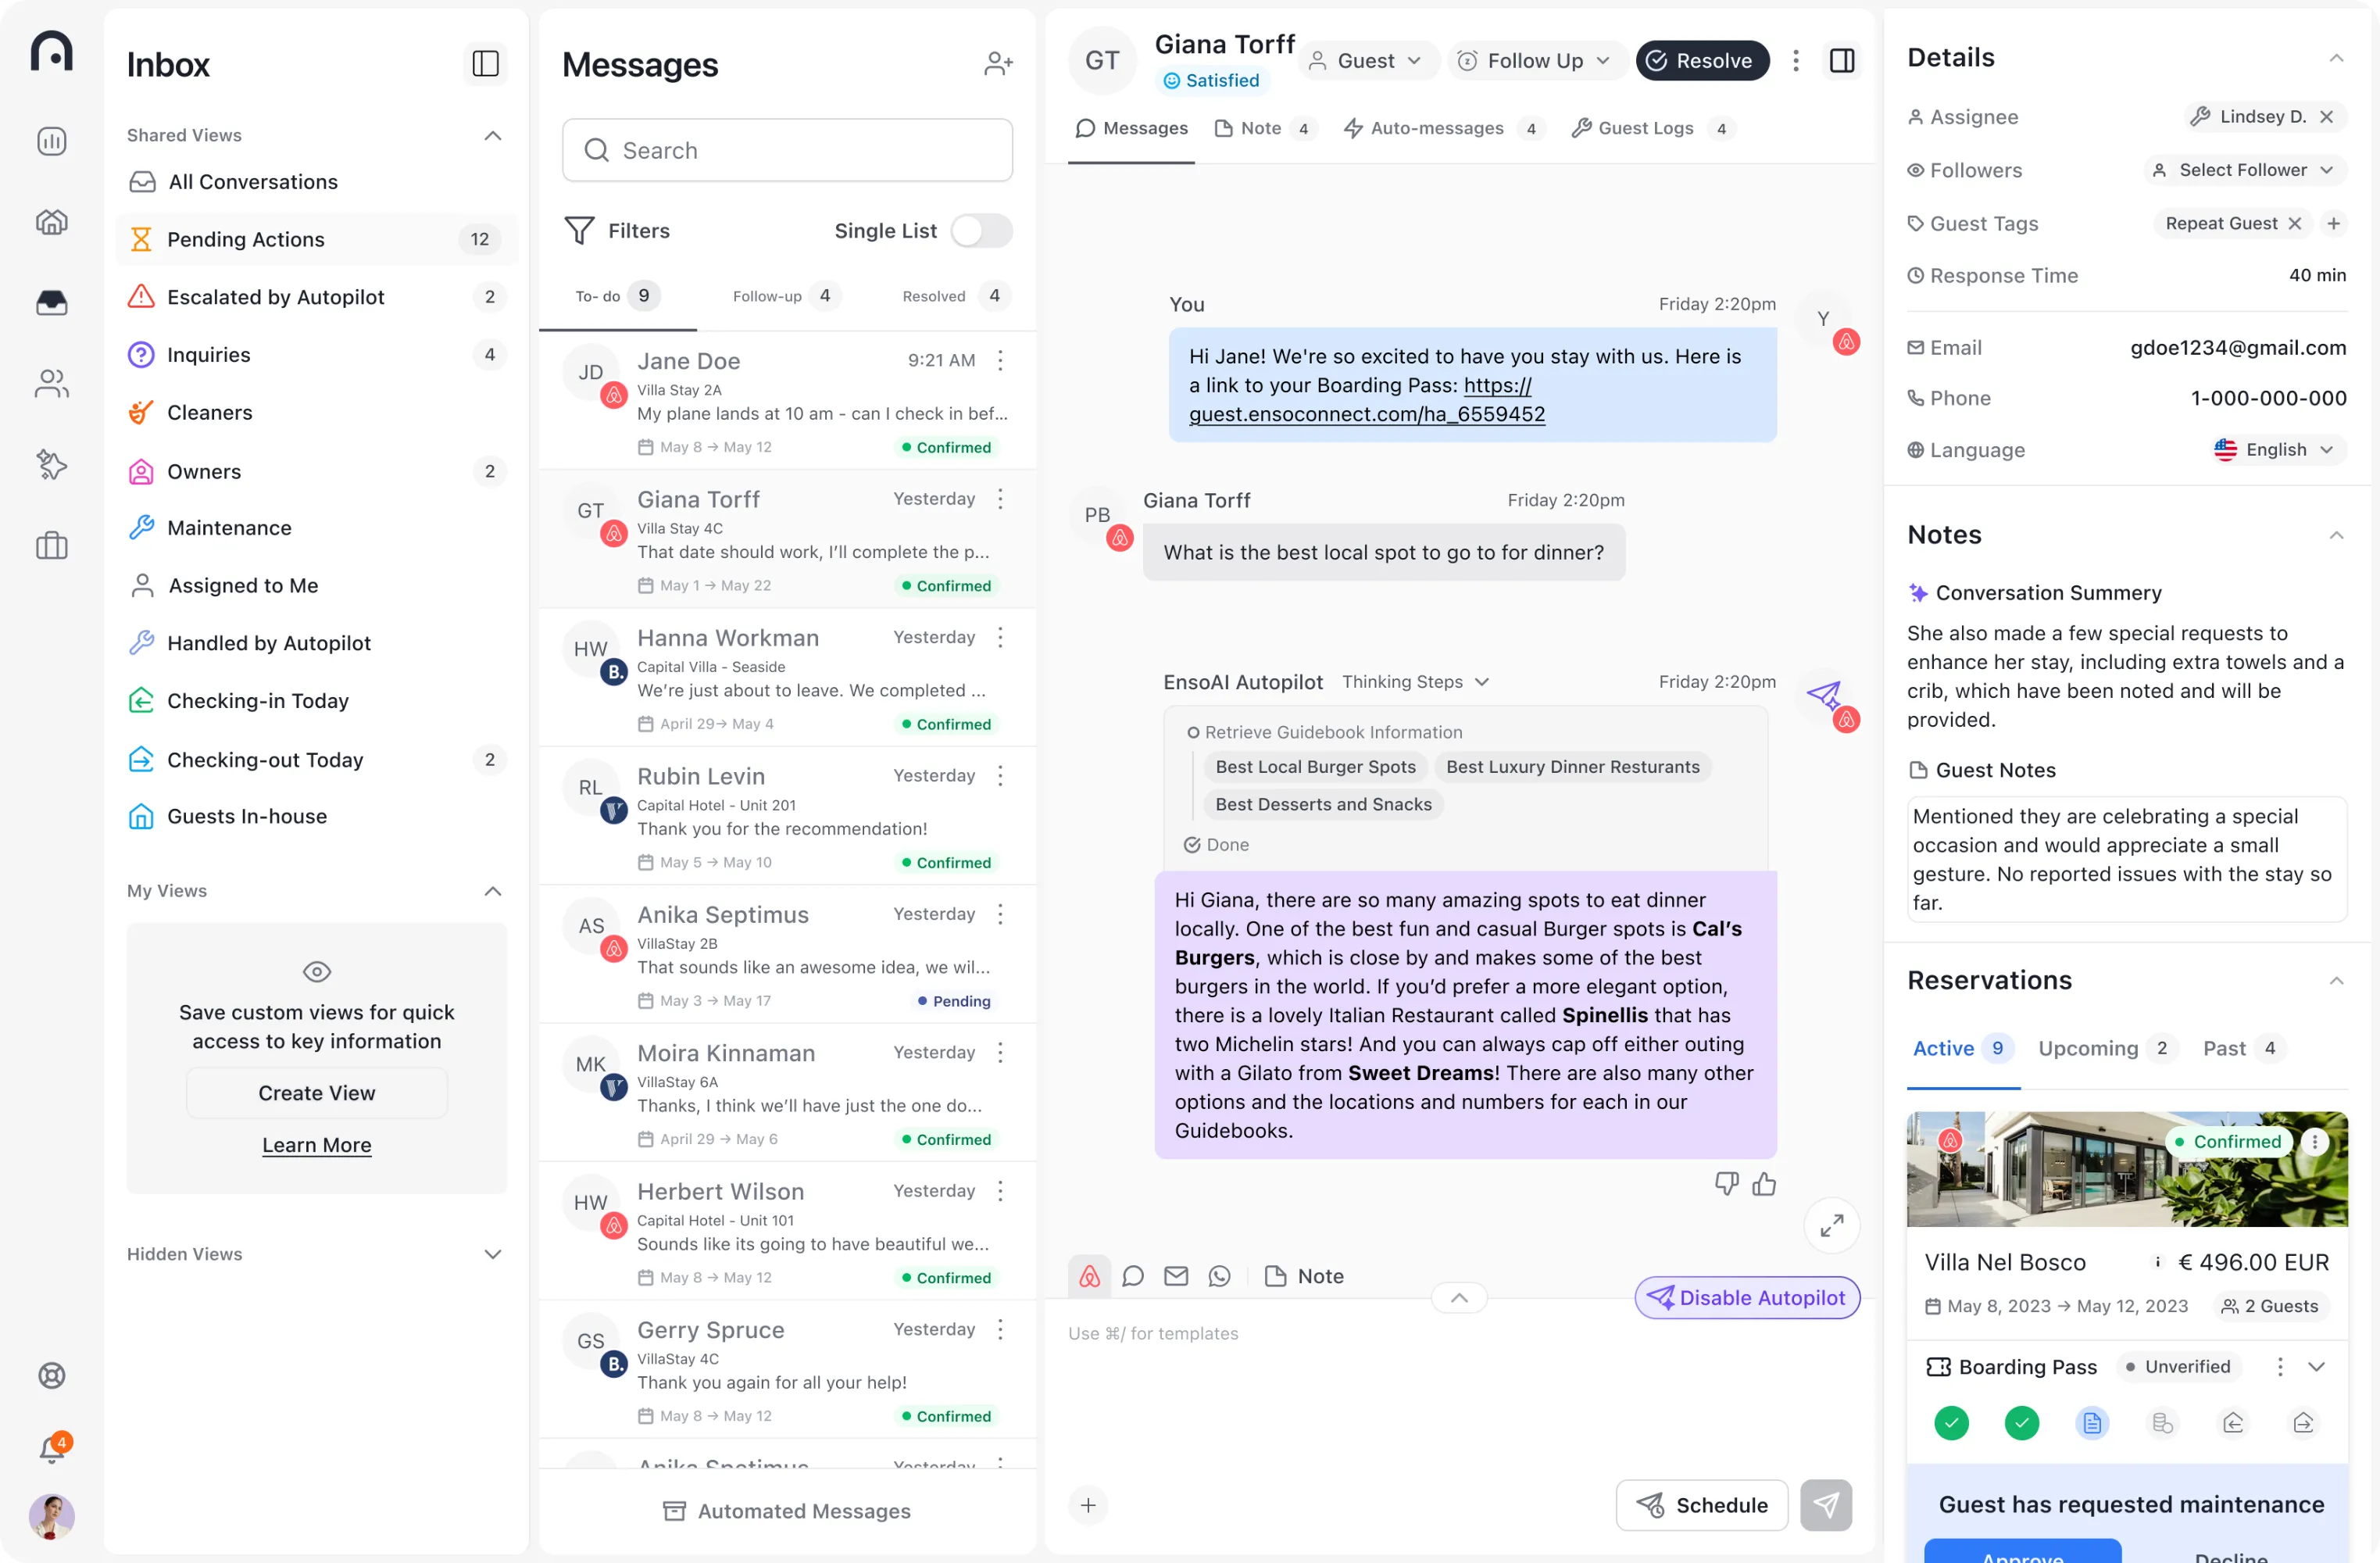
Conditional access ensures that property lock codes remain inactive until verification is complete. Enso Connect's boarding pass withholds access credentials until all pre-arrival requirements — verification, ID check, security deposit, signed agreement — are confirmed. A booking that's flagged for suspicious activity doesn't get access codes regardless of the scheduled check-in time.
Using IoT Data to Win Chargeback Disputes
Preventing fraudulent entry is the primary goal. But operators also need protection against verified guests who violate house rules after check-in and then dispute charges.
Enso Connect integrates with noise monitoring and environmental sensors to create an objective, privacy-compliant audit trail. These sensors track sustained noise levels and occupancy indicators without recording conversations or violating privacy laws. When a guest hosts an unauthorized gathering, the system logs the exact time the noise threshold was breached, the duration of the violation, and the automated warnings sent to the guest.
When that guest later files a chargeback claiming the property was misrepresented, operators can present timestamped sensor data showing the policy violation. Combined with the biometric identity and signed digital contract, this data package neutralizes false claims and dramatically improves dispute win rates.
Legal Considerations for Biometric Verification
Biometric verification must be implemented within the framework of applicable data privacy laws. Biometric data is classified as sensitive personal information in most jurisdictions, and operators have specific obligations around consent, storage, and use.
Enso Connect handles biometric data within enterprise-grade security infrastructure: all sensitive identity information is encrypted, tokenized, and automatically purged according to compliance frameworks. Operators don't store raw biometric data locally — the system manages retention and deletion automatically.
Transparent disclosure in your listing description and guest agreement is both a legal requirement and a practical deterrent. When bad actors see a property requires biometric liveness detection, they typically abandon the reservation and target easier victims instead.
Building Your Security Perimeter
For operators looking to implement a comprehensive fraud prevention approach, the recommended sequence is:
Start with digital contracts and conditional access — these have zero guest friction for legitimate bookings and immediately eliminate the class of fraudsters who abandon when confronted with any verification requirement. Add biometric liveness detection to close the deepfake vulnerability. Integrate noise monitoring to create the IoT audit trail needed for chargeback defense. Review your pre-arrival workflow to ensure verification must be completed before access credentials are released.
The fraud threat will continue evolving as AI tools become more accessible. Static verification methods — ID photo uploads, manual review, basic identity checks — will become increasingly insufficient. The operators who protect their properties and their revenue in this environment are those who build security perimeters that can't be defeated by a synthesized image.
Book a demo with Enso Connect to see guest verification in action.